
Third-Party Risk Management
Third-Party Risk Management (TPRM) is the process of identifying, assessing, monitoring, and managing risks introduced by suppliers, vendors, service providers, and other external parties.
Overview
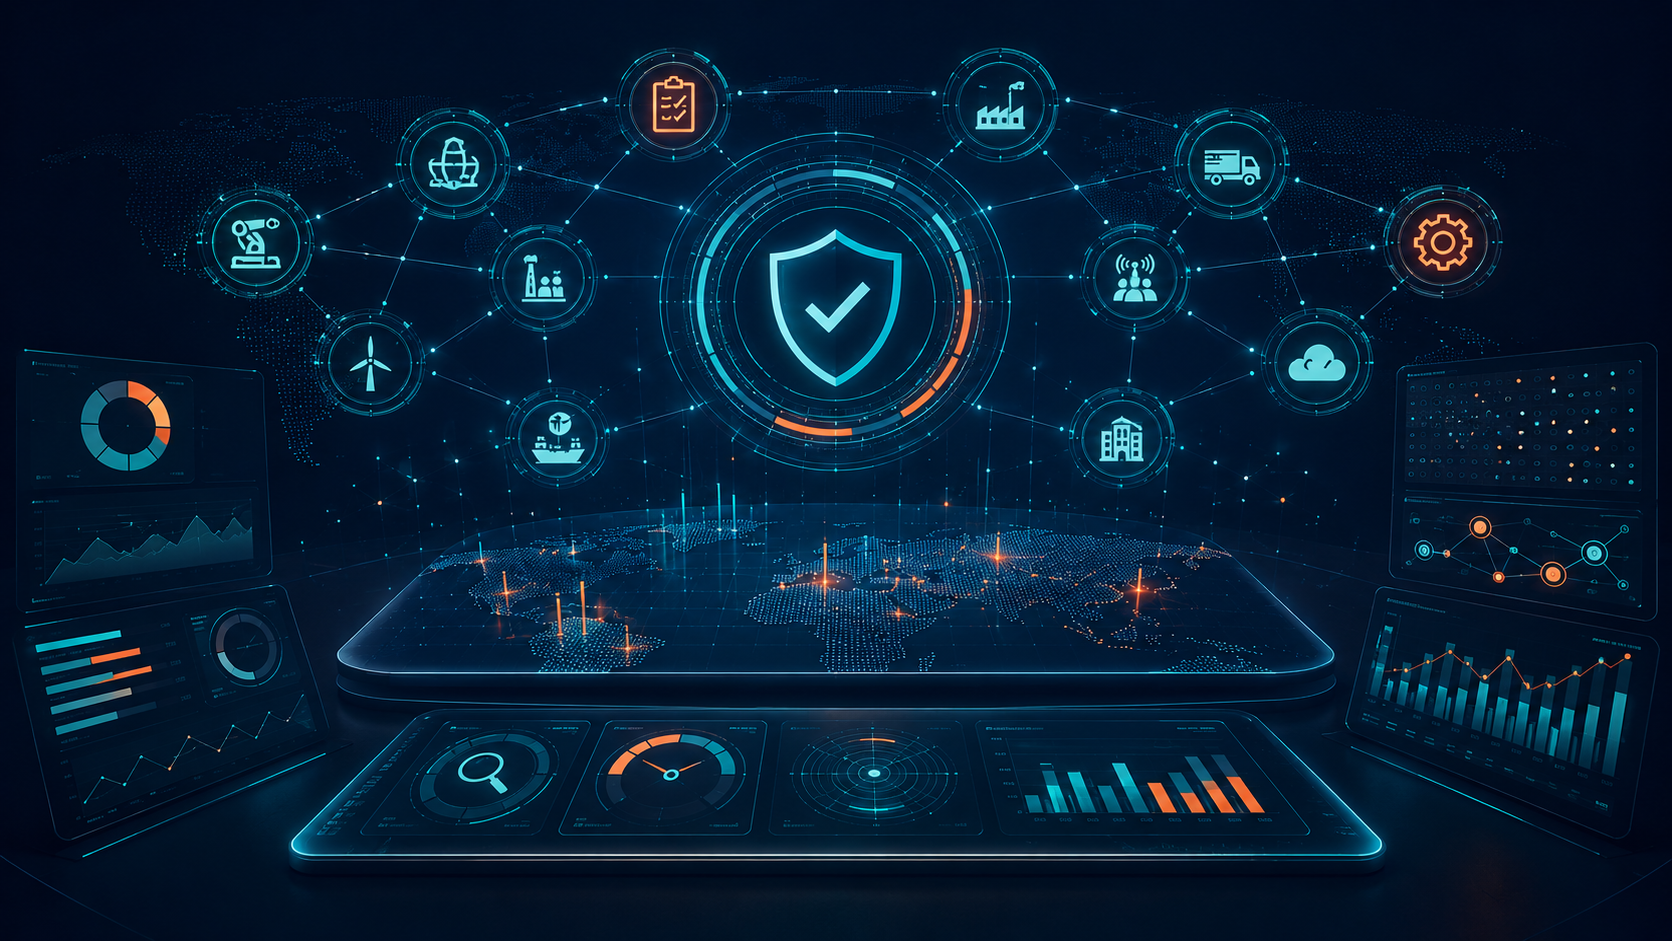
Third-Party Risk Management (TPRM) helps organizations identify, assess, monitor, and manage risks introduced by suppliers, vendors, service providers, and other third parties throughout the vendor lifecycle.
Updated
Definition
Third-Party Risk Management (TPRM) is the structured process of identifying, assessing, mitigating, monitoring, and governing risks associated with suppliers, vendors, contractors, partners, and external service providers.
Modern organizations increasingly depend on third parties for critical business operations, technology services, cloud infrastructure, data processing, professional services, and supply chain activities. While these relationships create business value, they also introduce security, operational, compliance, financial, and reputational risks.
TPRM provides a framework for understanding and managing these risks throughout the entire vendor lifecycle, from onboarding and due diligence through ongoing monitoring, contract renewal, and offboarding
Related guidance: Operational Resilience, Vendor Risk Management, Third-Party Assurance.
Why It Matters
Third-party incidents have become one of the most significant sources of operational disruption, cyber breaches, regulatory enforcement actions, and reputational damage.
Organizations are increasingly expected by regulators, customers, auditors, and boards to demonstrate effective oversight of suppliers and service providers.
A mature TPRM program enables organizations to make informed risk decisions, strengthen governance, reduce exposure, improve resilience, and maintain trust with stakeholders.
Key Challenges
- Lack of visibility into supplier risks
- Manual assessment processes and spreadsheets
- Inconsistent risk scoring and classification
- Limited monitoring after onboarding
- Growing regulatory requirements
- Managing fourth-party and supply chain dependencies
- Resource constraints within risk and security teams
- Difficulty demonstrating ongoing assurance to auditors and regulators
How TPSaaS Helps
TPSaaS supports Third-Party Risk Management by connecting supplier context, structured evidence, practitioner judgment, and accountable governance across the third-party lifecycle.
Teams can use risk-based assessments, evidence review, findings, ownership, and follow-up to support proportionate supplier decisions. Technology organizes the work; people interpret the evidence and remain accountable for the outcome.
Support for a framework does not establish certification or guarantee compliance. The applicable requirements, evidence, and decisions still need review in the organization’s context.
Business Outcomes
- Risk-based vendor onboarding and approval decisions
- Consistent assessment and review processes
- Improved consistency of risk decisions
- Enhanced supplier visibility and oversight
- Stronger operational resilience
- Improved compliance readiness
- Reduced exposure to cyber and supply chain risks
- Board and regulator-ready reporting
These are program aims, not guaranteed outcomes. Results depend on implementation, supplier evidence, practitioner review, and accountable decisions; using TPSaaS does not establish certification or guarantee compliance.
Regulatory Relevance
Third-Party Risk Management supports compliance and resilience objectives across multiple regulations and frameworks including:
- DORA
- NIS2
- ISO/IEC 27001
- SOC 2
- PCI DSS
- GDPR
- UK Operational Resilience requirements
- UK Critical Third Party expectations
- Industry-standard supplier assurance practices
Applicability depends on the organization, service, and jurisdiction. Regulations, supervisory guidance, voluntary standards, and assurance reports have different roles; the list above is not a statement that every requirement applies to every supplier.
Primary references: DORA, including ICT third-party risk in Articles 28–30; NIS2, including supply chain security in Article 21; FCA operational resilience guidance.
Frequently Asked Questions
What is Third-Party Risk Management?
Third-Party Risk Management is the process of identifying, assessing, monitoring, and managing risks introduced by suppliers, vendors, and service providers.
Why is Third-Party Risk Management important?
Organizations increasingly depend on third parties to deliver critical services, making supplier risk management essential for security, resilience, compliance, and business continuity.
What risks are covered by TPRM?
TPRM addresses cybersecurity, operational, compliance, financial, legal, reputational, privacy, and resilience-related risks.
What is the difference between TPRM and Vendor Risk Management?
Vendor Risk Management is typically considered a subset of the broader Third-Party Risk Management discipline, which covers all external relationships and dependencies.
How does TPSaaS support TPRM?
TPSaaS connects supplier context, evidence, practitioner judgment, and accountable decisions. It supports assurance work; it does not guarantee compliance or replace human review.

Put this guidance into practice
Explore how TPSaaS connects supplier context, evidence, practitioner judgment, and accountable decisions across the third-party lifecycle.